.webp)
.webp)
.webp)
.webp)
Cost Optimization
Optimizing AI Resource Utilization and Expenditure
Engineered token-level cost analysis, prompt-efficiency assessment, and model-selection logic to identify inefficient usage patterns and reduce avoidable AI expenditure.
Forward Deployed
Engineering
Extend your team with engineers embedded in your workflows.
HIRE DEDICATED ENGINEERS
Need Help Choosing the
Right Service?
Share your idea, challenge, or requirement with our experts.
ASK EXPERTS
Planning an Industry-
Focused Product?
We'll help you define the right technology approach for your market and users.
TALK TO EXPERTS Want to Build
Something Similar?
Explore how we've built AI products, platforms, and digital solutions across real business use cases.
VIEW WORKLangProtect
Quokka Labs engineered LangProtect's modular AI security platform from architecture to production. Our engineers built runtime threat detection, sensitive data redaction, shadow AI governance, and MCP agent access control into one platform, covering AI applications, employee AI usage, and autonomous agents.
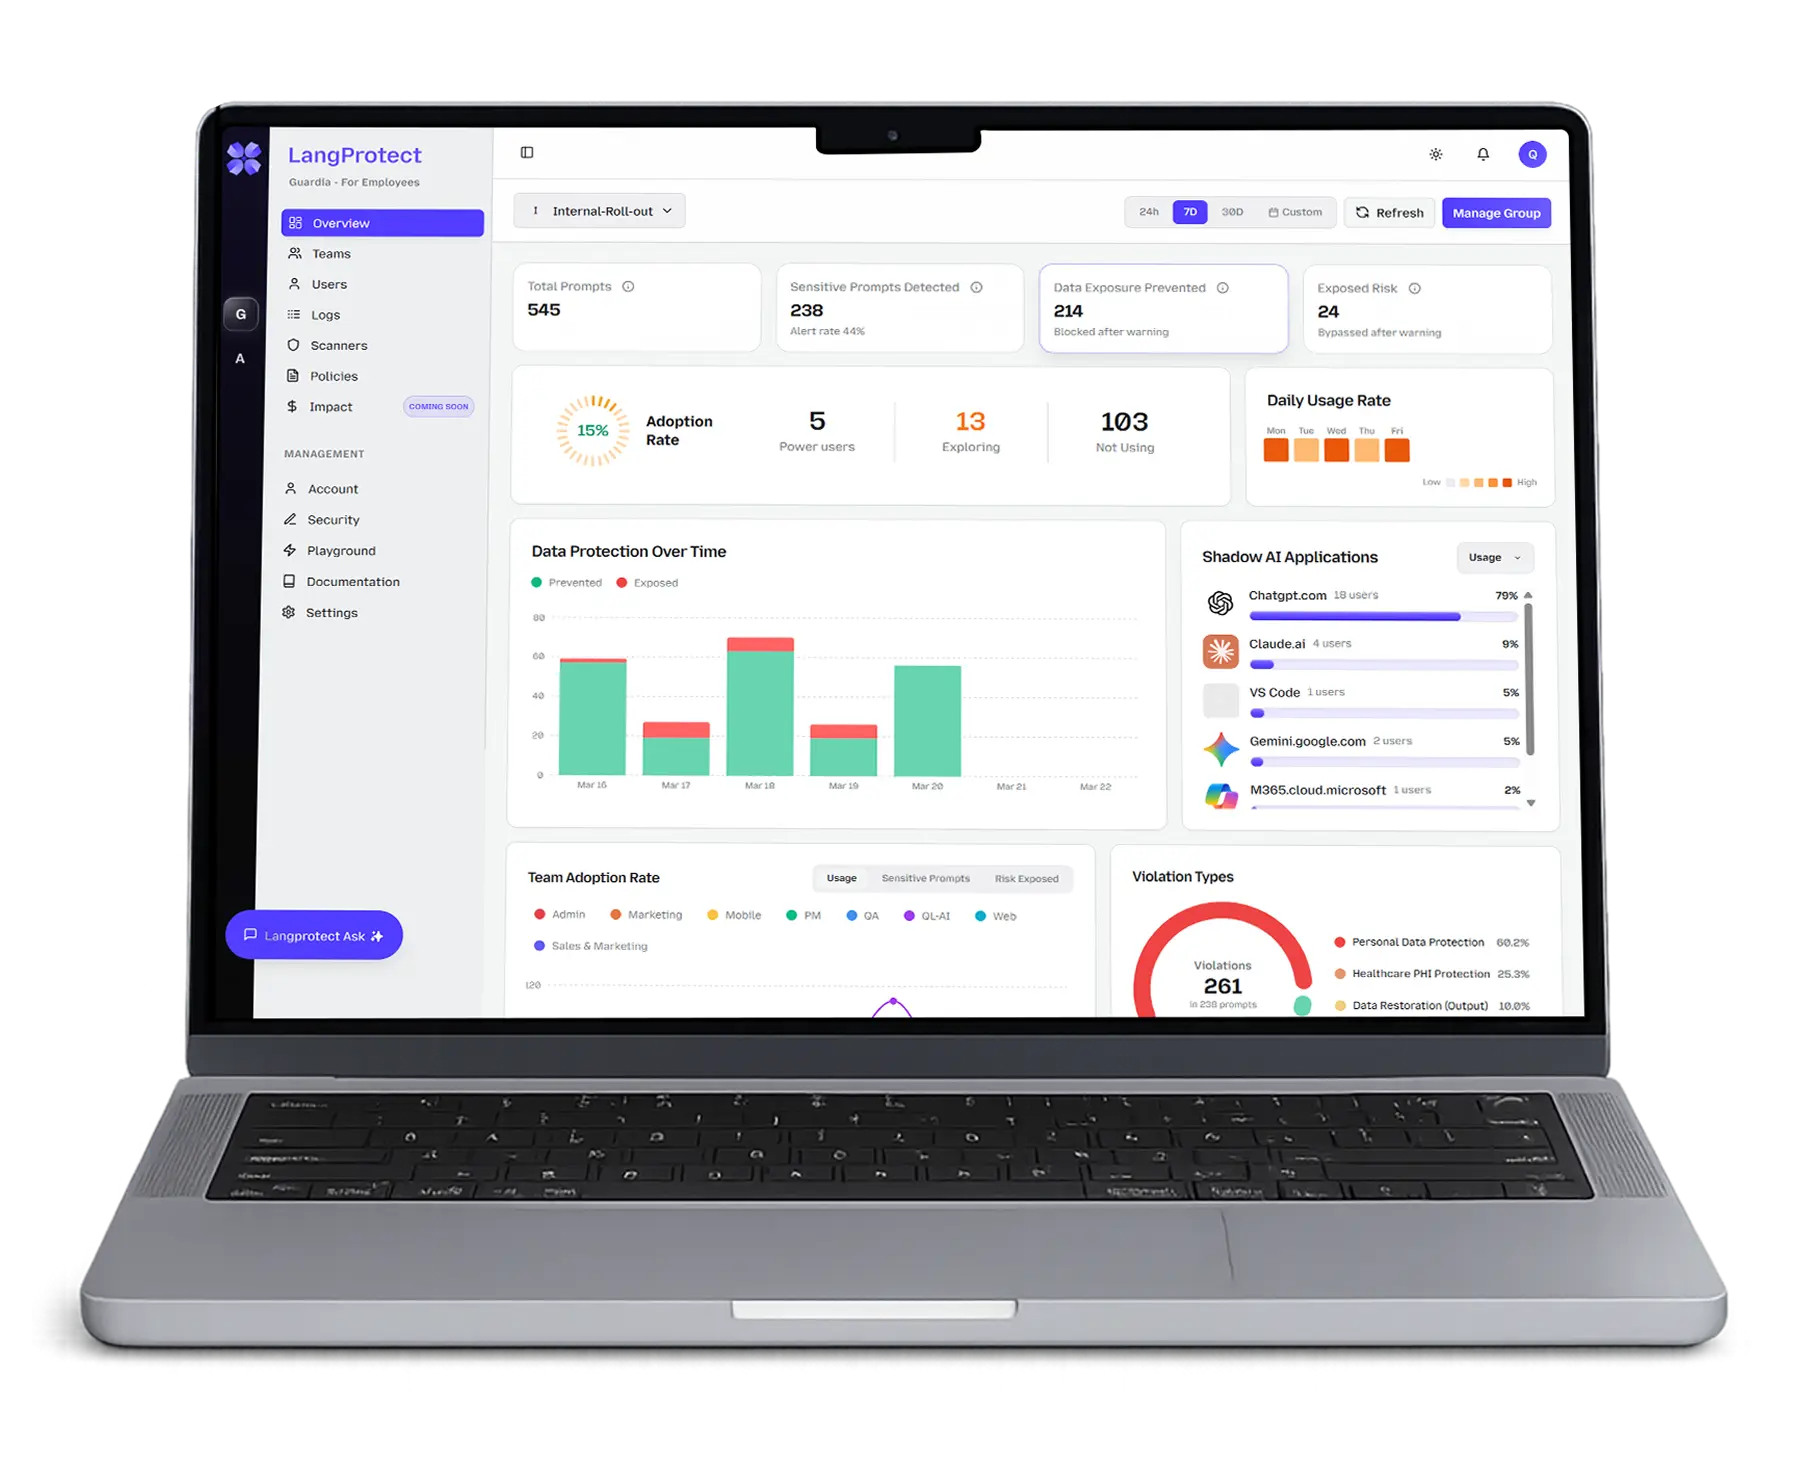
LangProtect helps enterprises adopt generative AI without exposing sensitive data. To turn that vision into a production platform, LangProtect partnered with Quokka Labs, and our engineers designed and built four specialized security modules.
Quokka Labs engineered integrated AI security controls to protect sensitive data, detect emerging threats, govern agent access, and strengthen oversight across workforce AI usage and application workflows.
Problems
AI applications require protection against prompt injection, jailbreaks, and sensitive data leaks without introducing disruptive latency into conversational workflows.
Solutions
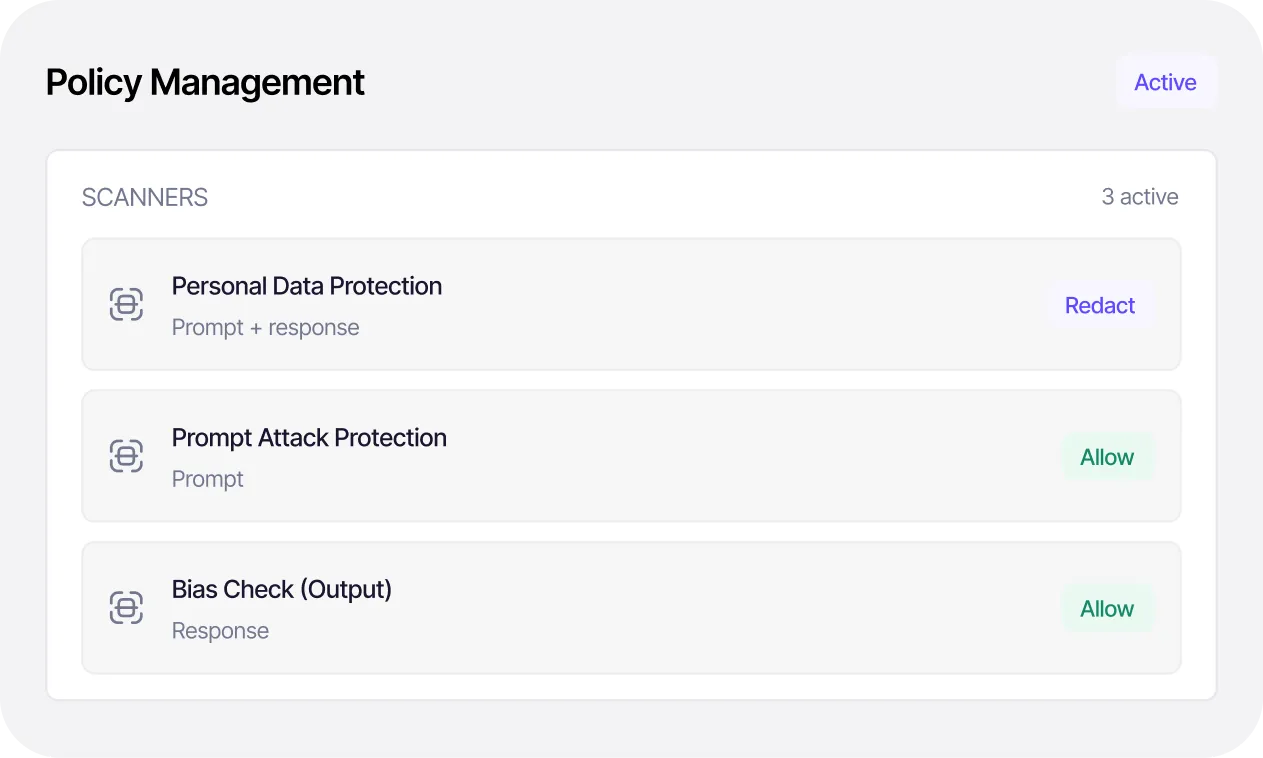
Quokka Labs engineered a centralized Policy Engine and API that run specialized scanners, in parallel on every prompt and response, returning allow, redact, or block verdicts without stalling the conversation.
Problems
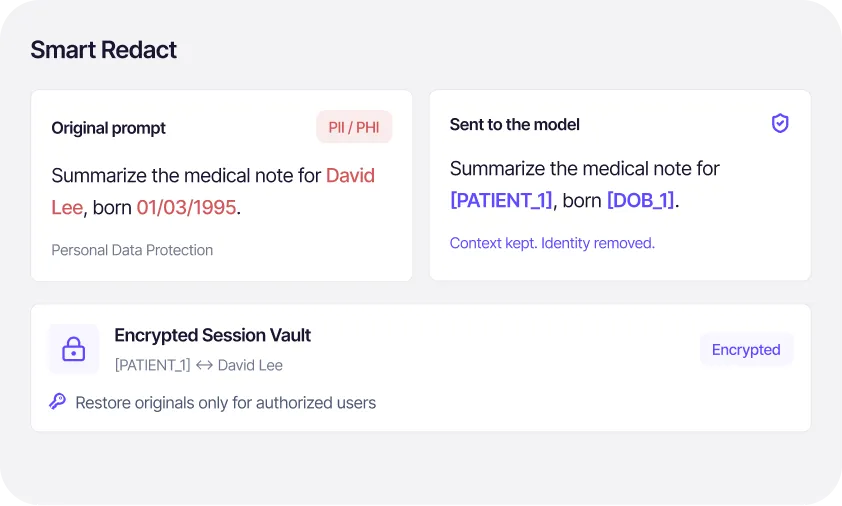
Redacting PII and PHI can disrupt conversational context, reduce model response accuracy and limiting the usefulness of sensitive data workflows.
Solutions
Our engineers built Smart Redact to swap PII and PHI for context-aware placeholders before prompts reach the model, and an encrypted Session Vault that restores original values only for authorized users.
Problems
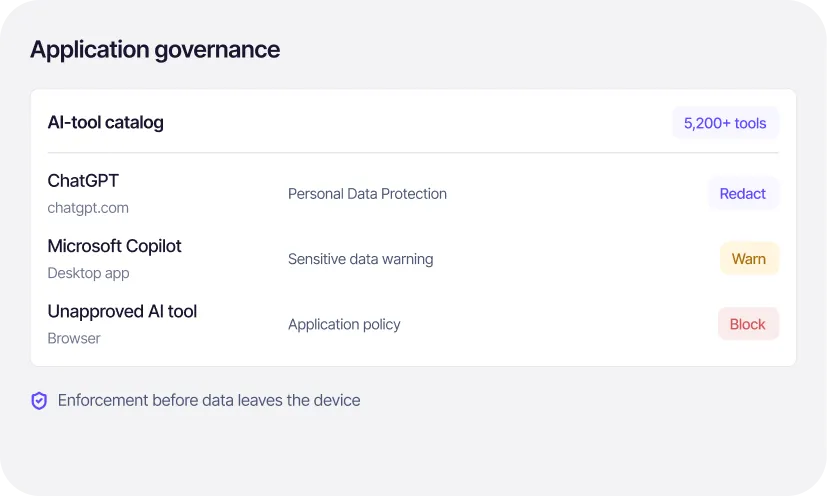
Employees can expose confidential records, proprietary source code, and credentials through unapproved AI tools operating beyond centralized security visibility.
Solutions
We engineered browser and desktop monitoring agents, a catalog of 5,200+ AI tools, and automated policies that warn, redact, or block before data leaves the device.
Problems
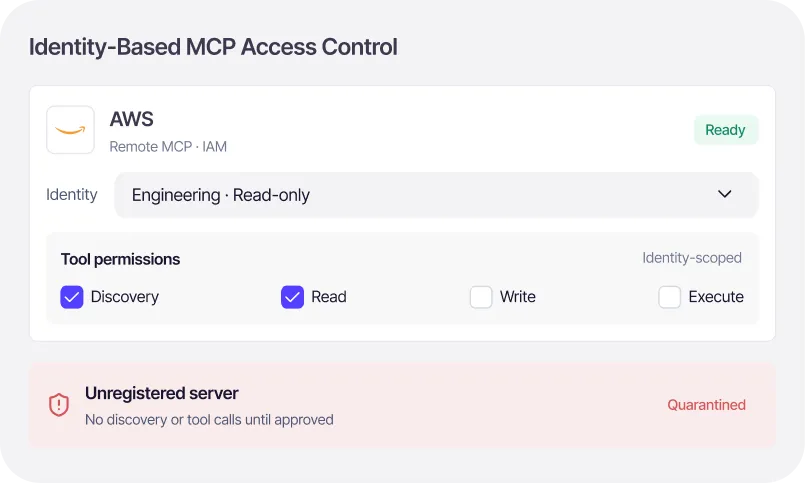
AI agents and Non-Human Identities (NHIs) can inherit excessive tool permissions, enabling unauthorized discovery, data access, modifications, or execution.
Solutions
Our team engineered MCP-layer authorization with granular discover, read, write, and execute permissions, plus quarantine workflows for unregistered MCP servers.
Problems
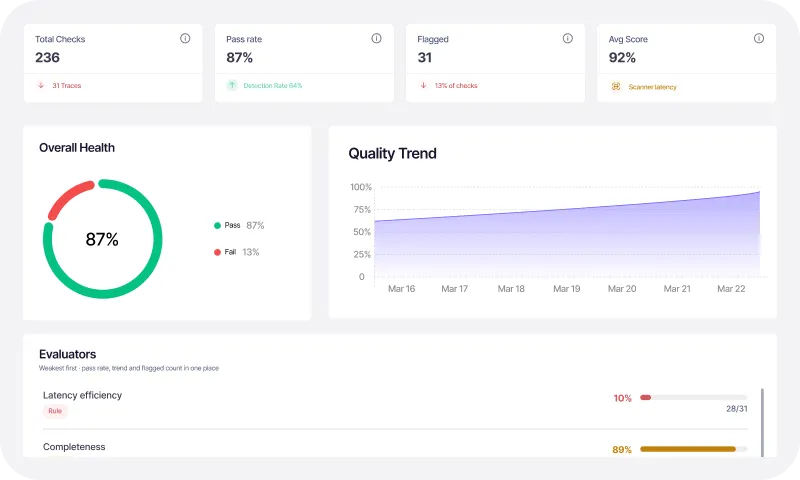
Limited trace visibility obscures hallucinations, response quality, latency, token waste, and unnecessary model spend across production AI applications.
Solutions
AI experts developed Trace, Evaluations, and cost analytics to measure latency, token usage, response quality, hallucinations, and model expenditure.
We mapped security requirements across AI applications, workforce usage, and autonomous agents, defining a modular architecture for Armor, Guardia, Vector and AI red teaming.
We engineered runtime inspection, workforce monitoring, Smart Redact, and encrypted session storage to protect sensitive data across AI interactions.
We engineered a framework of 32+ specialized scanners and built MCP-layer authorization so new scanners and permission rules can be added without redeploying the platform.
We developed Trace, Evaluations, and usage analytics to measure response quality, latency, token consumption, and potential data exposure across AI workflows.
We tested the platform against adversarial prompt-injection and jailbreak test sets, benchmarked redaction accuracy across PII, PCI, PHI and financial entities types, and load-tested inspection latency before launch.
We supported LangProtect's production launch with onboarding flows, application integrations, and policy templates, and continue to ship improvements based on live security events.
Prompts Detected
Sensitive Data Coverage
AI Tools Covered by Discovery
MCP Servers Covered by Authorization
Quokka Labs engineered integrated AI security controls, covering runtime threat detection, sensitive data protection, workforce AI governance, and agent authorization to address complex risks across organizational AI environments.
Optimizing AI Resource Utilization and Expenditure
Engineered token-level cost analysis, prompt-efficiency assessment, and model-selection logic to identify inefficient usage patterns and reduce avoidable AI expenditure.
Measuring AI Behavior, Quality, and Performance
Developed trace-level monitoring and AI evaluation methods to assess model responses, latency, token consumption, cost, factual accuracy, and hallucination patterns.
Identifying Vulnerabilities Through Adversarial AI Testing
Engineered AI red teaming and adversarial testing workflows to assess LLMs, RAG pipelines, and AI agents against prompt injection, jailbreaks, system-prompt extraction, and other AI-specific attack scenarios.
Preventing Confidential Data Exposure to AI Models
Engineered contextual data redaction and session-level value restoration to protect personal, medical, and financial information while preserving conversational context.
Identifying Unapproved AI Adoption Across Teams
Developed AI tool discovery and endpoint monitoring, delivered through a lightweight browser extension and desktop agent, to identify unapproved applications, surface workforce AI usage patterns, and enforce policies before data loss.
Detecting and Controlling Threats in Live AI Applications
Engineered prompt and response inspection, specialized threat detection, and policy-driven enforcement to address prompt injection, jailbreaks, toxic content, and sensitive data exposure.
Controlling Access Across MCP-Based Agent Workflows
Developed identity-linked authorization for AI agent workflows and connected tools, applying granular discovery, read, write, and execute permissions to restrict unauthorized agent actions.
Establishing Evidence for Security Reviews and Investigations
Engineered audit logging to record detections, policy decisions, enforcement actions, authorization events, and AI security activities, supporting investigations and internal reviews through AI compliance and audit automation.
Translating Security Signals Into Actionable Risk Insights
Engineered pipelines that structure threat signals, scanner results, and security events to identify recurring attack patterns, investigate suspicious activity, and inform improvements to AI security policies.
Quokka Labs helps organizations engineer AI-powered products, modernize legacy systems, and automate complex workflows to unlock measurable business value.
Run The Day (RTD)
AI-Enabled Event Management Platform
70%
Faster Task Completion
50%
Fewer Setup Errors
Rhubarb
AI Gardening Assistant
50%
Fewer Crop Failures
27%
Higher Harvest Yields
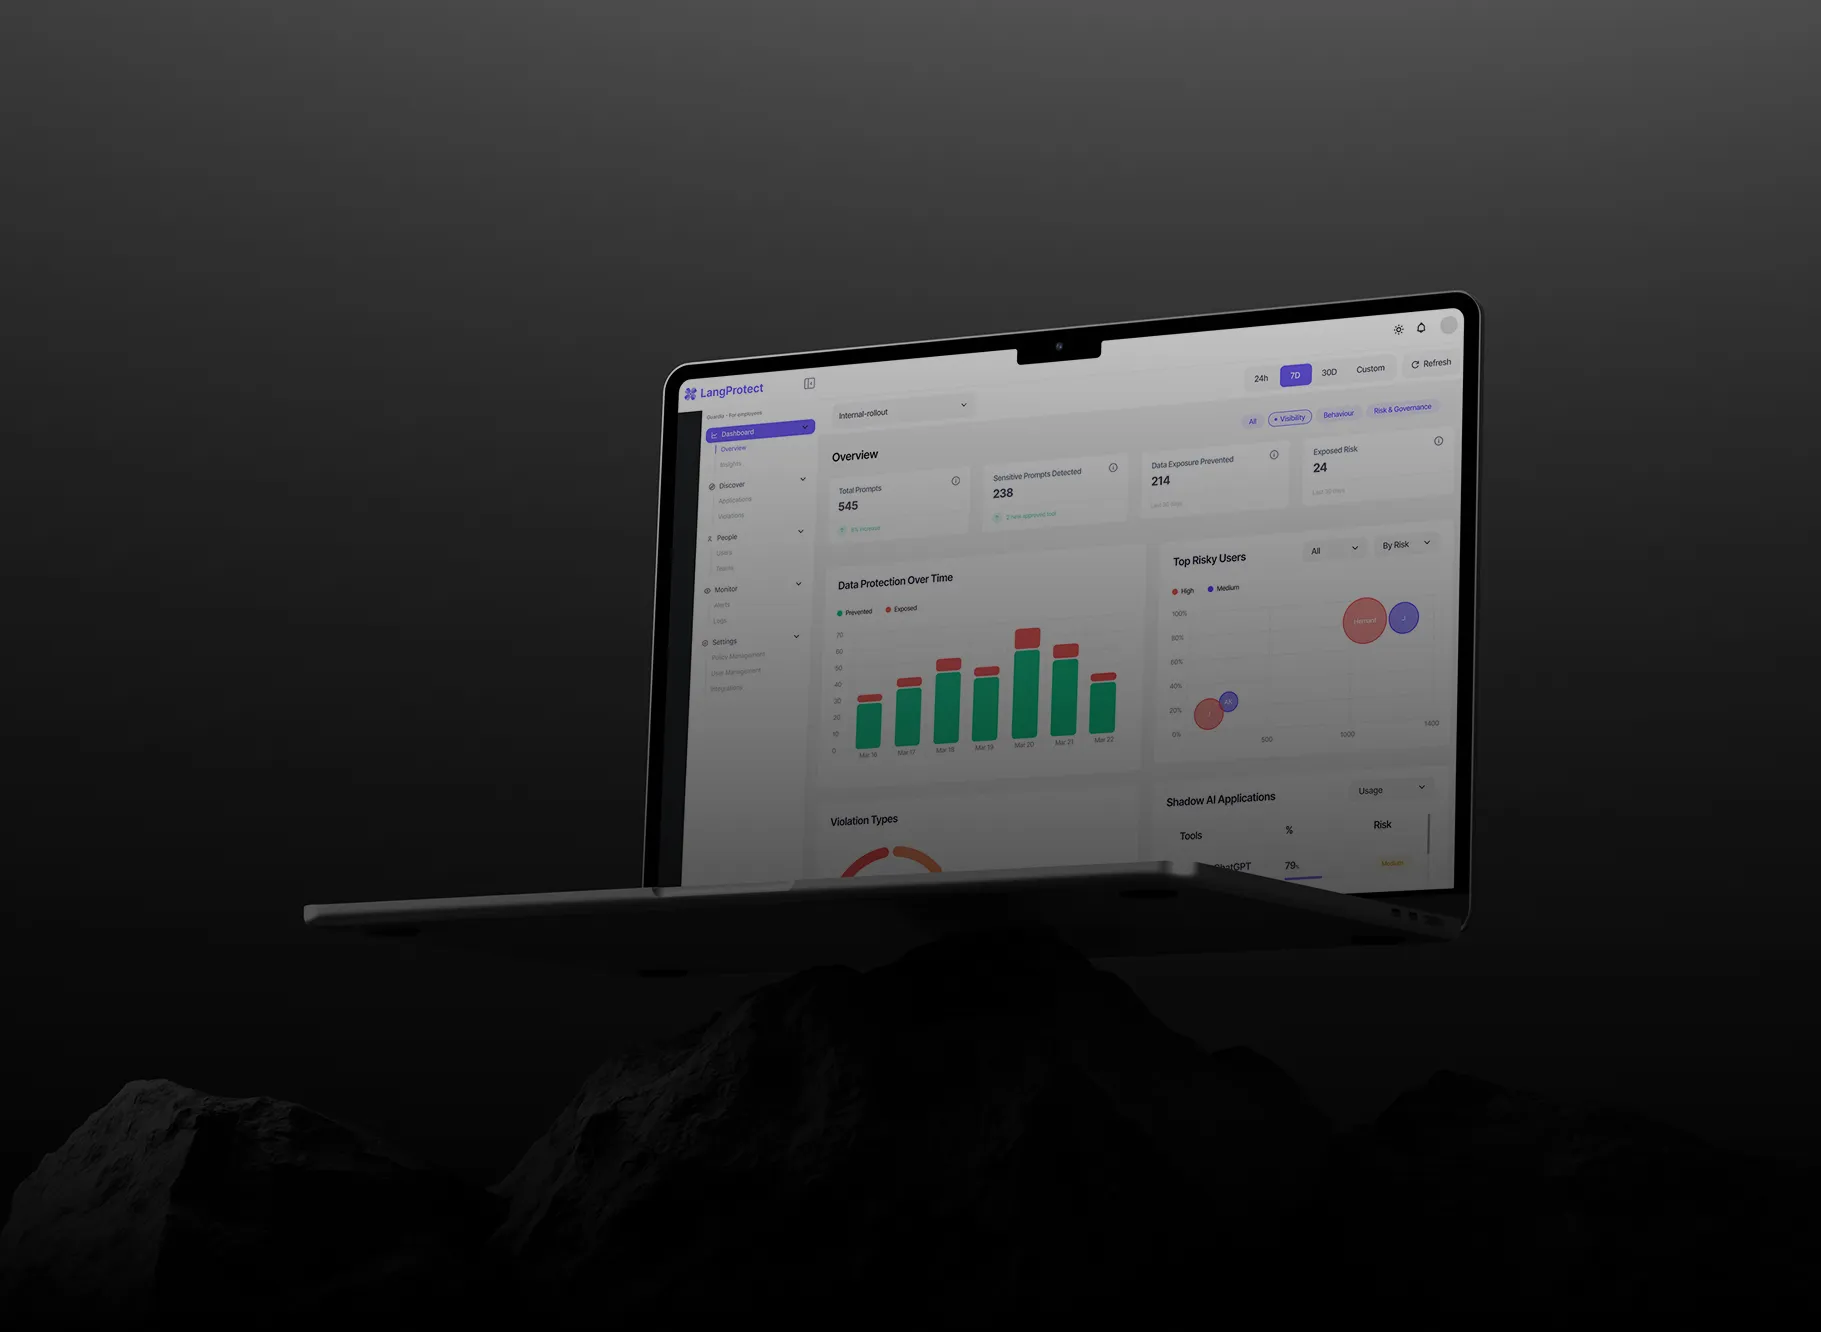
LangProtect
AI Security and Governance Platform
70%
Better AI Activity Visibility
55%
Faster Governance Response
Sniper
Automated Lead Generation Platform
70%
Faster Lead Acquisition
90%
Higher Lead Relevance
Whisperr
AI-Driven Secure Communication Platform
100%
Encrypted Communication
60%
Faster Response Times
WriteEasy
AI Writing Assistant
30%
Better Writing Efficiency
80%
Faster Content Creation
UG Floor, Tower-4, Assotech Business Cresterra, Plot No.22, Sector-135, Noida, Uttar Pradesh, 201305
111 Congress Avenue Suite 500, Austin,
Texas - 78701
Jasmijnlaan 88, 1187 EL Amstelveen,
Netherlands